> ## Documentation Index
> Fetch the complete documentation index at: https://university.triggr-app.com/llms.txt
> Use this file to discover all available pages before exploring further.
# ThreatLocker
> Connect ThreatLocker to Triggr with the API token of a ThreatLocker API user.
Triggr works with ThreatLocker computers, maintenance mode, approval requests, logs and audits, applications, policies, tags and scheduled agent actions.
## Set up ThreatLocker
In **Users > Roles**, click **+ New Role**, name it `Triggr`, tick the permissions your workflows need and click + Create Role. Create it in the organisation where you'll create the API user.
| Workflows will | Permissions |
| - | - |
| Find and read computers | View Computers |
| Edit, restart, rescan, or enable or disable protection | Edit Computers |
| Change maintenance mode | Edit Computers plus that mode's permission, such as Manage All Maintenance Modes |
| Read approval requests | View Approvals |
| Approve applications | Approve for Entire Organization, Approve for Group or Approve for Single Computer, plus Approve for New Install or Approve for Update Existing. Elevation also needs Elevation Administrator. |
| Read or generate an auth key | Edit Computers and Install Computers |
Other endpoints list their permissions under Help > API Documentation in the portal. See ThreatLocker's [user permissions](https://threatlocker.kb.help/user-permissions/) guide.
Select the Manage icon, go to **Users > API Users** and click **New API User**. Name it `Triggr` with Basic Authentication (API Token), not OAuth 2.0; click Generate API Token and copy the token (ThreatLocker won't show it again); add the `Triggr` role and leave Organization empty to cover every organisation. Tick Accept EULA and click Create. See ThreatLocker's [API Users](https://threatlocker.kb.help/api-users/) guide.
Select Help in the portal. Your instance letter, such as `g`, is next to ThreatLocker Access. See [Locating Your Organization's Instance](https://threatlocker.kb.help/locating-your-organizations-instance/).
## Connect it in Triggr
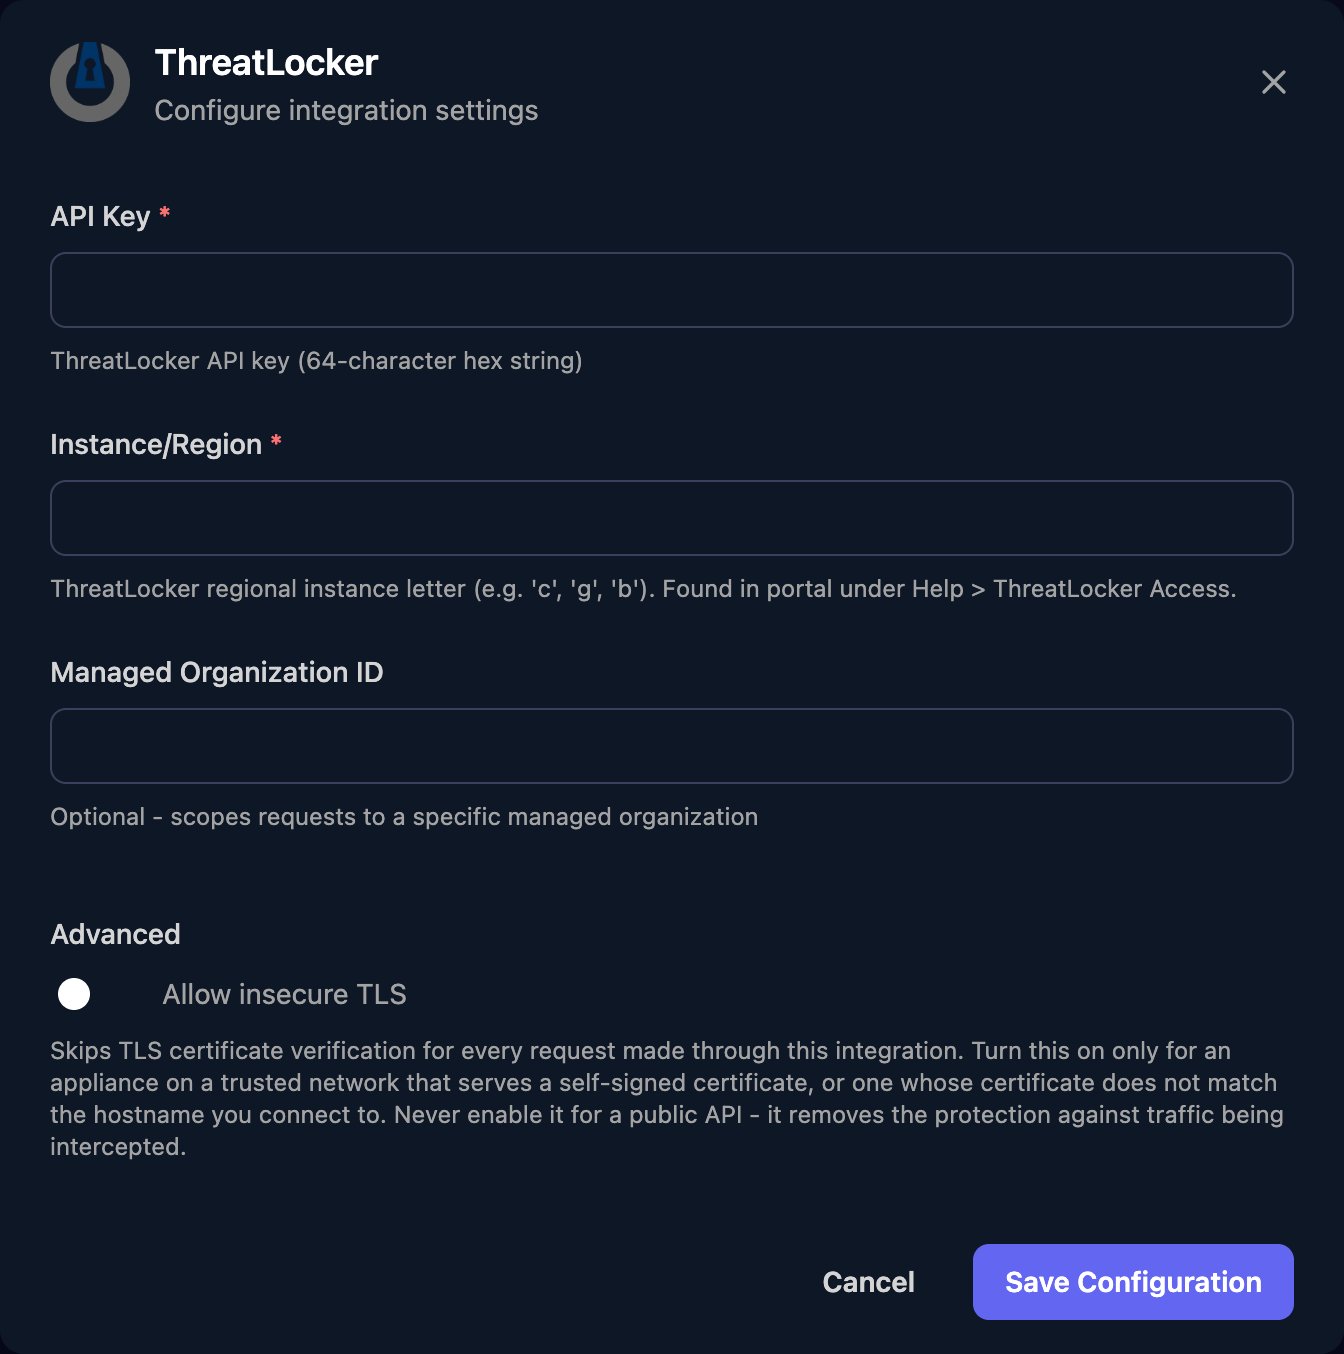
Go to **Integrations > ThreatLocker** and click **Configure** on the Base Configuration card.
 Paste the token alone into API Key, with no `Bearer`, and enter just the letter as Instance/Region. Leave Managed Organization ID blank to work in the API user's own organisation, or enter an Organization ID (from Manage > Organizations) to scope Triggr to that one. Click Save Configuration.
 There's no client mapping. To work across clients' organisations, create the API user in your top-level organisation with the role in every organisation and leave Managed Organization ID blank; many actions then take an organisation ID or a child-organisations option, such as `childOrganizations` on List Computers.
## Troubleshooting
ThreatLocker didn't accept the token. Check Instance/Region matches the letter under Help, API Key holds the full token alone, and the API user uses Basic Authentication (API Token).
The `Triggr` role lacks a permission the endpoint needs. Add it, then retry.
Managed Organization ID scopes every action to that organisation. Otherwise, add the role to more organisations, and use View Computers rather than View Computers - Managed Organization Only.
In Users > API Users, use Reset API Token on the `Triggr` user and copy the new token. In Triggr, click Edit on the Base Configuration card and paste it into API Key.
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.