

Set up Inforcer
1
Open the REST API settings
In the Inforcer portal, go to Configure and open REST API.
2
Create a key
Create a key covering every tenant your workflows use, with read access to the areas they use, plus permission to run assessments and reports if they start them. Triggr can only reach what the key covers.
3
Copy the key
Copy the key, and note the region your account is hosted in: ANZ, EU, UK or US.
Connect it in Triggr
1
Open the integration
Go to Integrations > Inforcer and click Configure on the Base Configuration card.
2
Enter the key and region
Paste the API Key, select your account’s Region and click Save Configuration.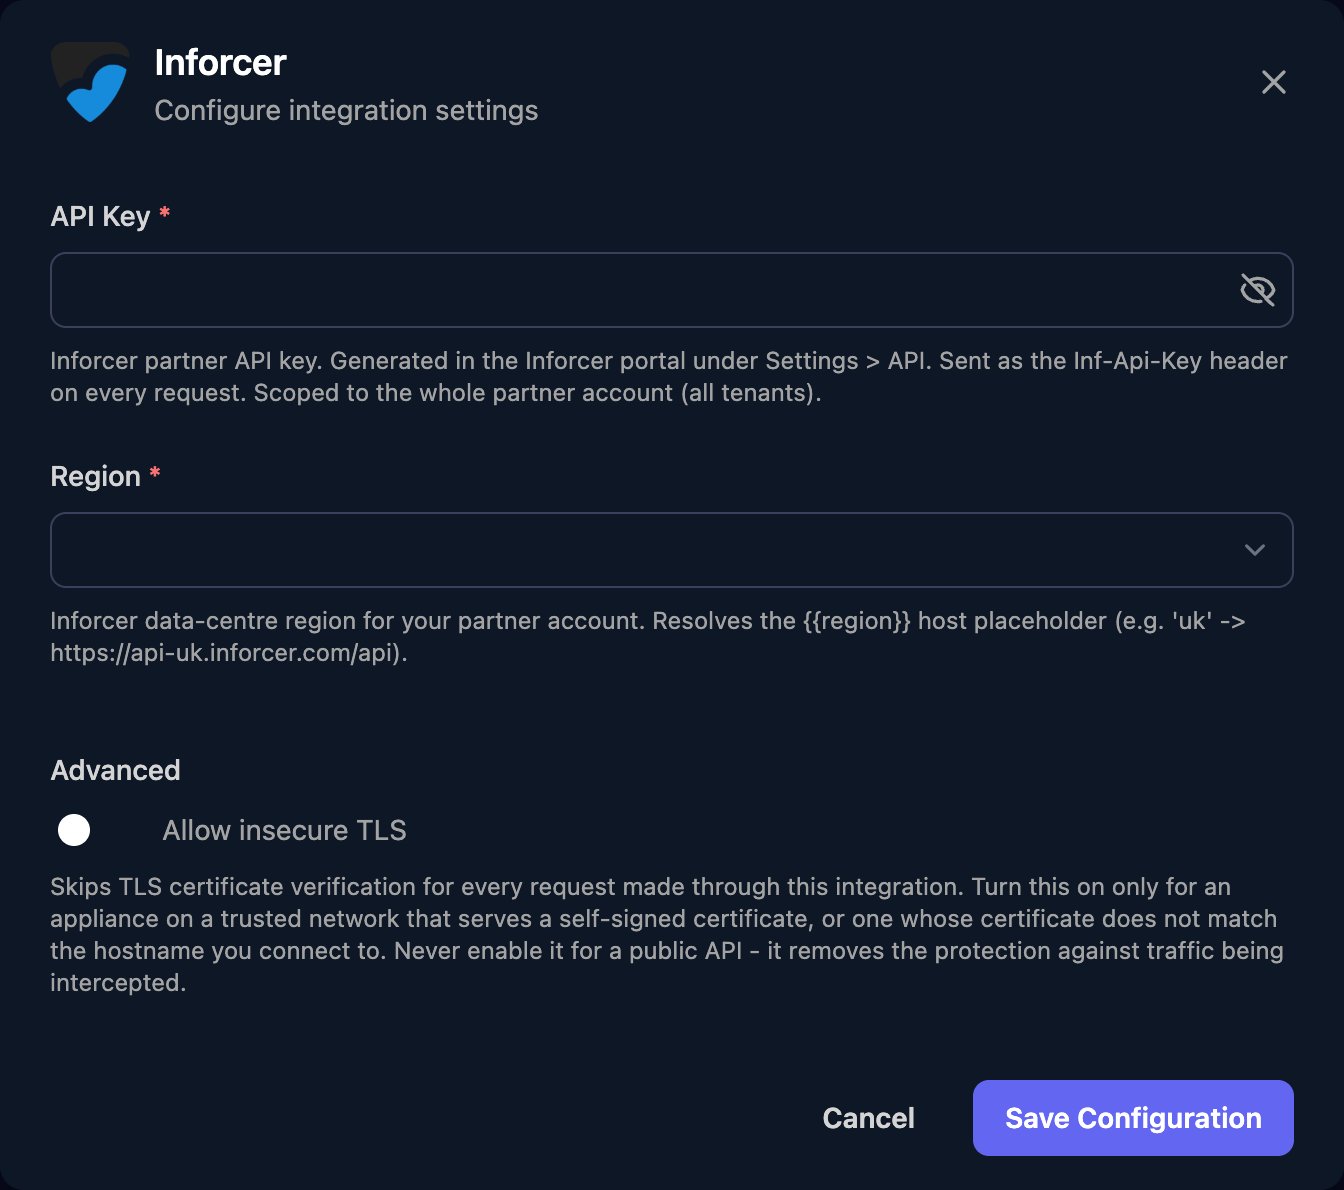
tenantId, a number that List Tenants returns as clientTenantId (not the Microsoft tenant ID). For paged results, pass each response’s continuationToken back in the next call.
Troubleshooting
Authentication errors (401)
Authentication errors (401)
Check the key was pasted in full and Region matches your account: a key only works in its own region. If the key was deleted, create a new one and paste it in with Edit on the Base Configuration card.
Permission errors (403)
Permission errors (403)
The key doesn’t cover that area or tenant. Create a new key with the right tenants and permissions.
Report outputs not found (404)
Report outputs not found (404)
Use List Report Runs to check the run is
completed or completedWithErrors first. The key must cover every tenant in the run.